The start of this thread is “number one reason people don’t move to Jellyfin is ease of remote access.”
30 years ago I was compiling slackware and configuring dns servers, and setting up BGP on Ciscos. But a few hours of attempting to setup Jellyfin was a failure. It was far more complex than setting up dns/bind.
Not at Cisco. With a Cisco. I ran a mid sized ISP in the 90’s until I was bought out by a cable company and retired. Although several of my employees went on to work at Cisco. I also had a few friends who were executives at Cisco because we all started at a company working for Vint Cerf and Bob Khan (they were the angel investors) back before most knew of the Internet.
First it’s a VM because I’m not going mess around with stuff on bare metal. Create docker is a can of worms because you have to pick a reverse proxy software like nginx, traefik, caddy. Which means you need to understand all three to know which to pick. Then there’s setting up the certificate with the dns provider. So I got nginx working with a certificate but gave up after the VM running Jellyfin couldn’t see it. Googling showed someone on Reddit with the same problem but no answer other than others saying “works for me”
Beside, that wasn’t even the topic. We were discussing - or rather, I was proving to the above commenter - that setting up Jellyfin in a way that does not allow an intruder to crypto mine or host CSAM or use your device as a proxy, is incredibly easy.
Port setup and it’s perceived impossibility by you has naught to do with that topic.


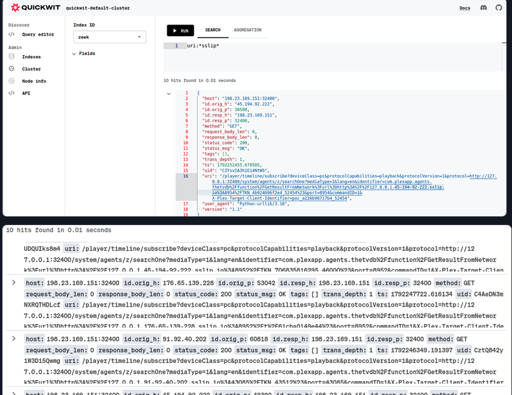
The start of this thread is “number one reason people don’t move to Jellyfin is ease of remote access.”
30 years ago I was compiling slackware and configuring dns servers, and setting up BGP on Ciscos. But a few hours of attempting to setup Jellyfin was a failure. It was far more complex than setting up dns/bind.
It’s literally just:
I highly doubt that if somehow you were setting up BGPs at Cisco, this incredibly straightforward port setup somehow got the best of you.
Not at Cisco. With a Cisco. I ran a mid sized ISP in the 90’s until I was bought out by a cable company and retired. Although several of my employees went on to work at Cisco. I also had a few friends who were executives at Cisco because we all started at a company working for Vint Cerf and Bob Khan (they were the angel investors) back before most knew of the Internet.
First it’s a VM because I’m not going mess around with stuff on bare metal. Create docker is a can of worms because you have to pick a reverse proxy software like nginx, traefik, caddy. Which means you need to understand all three to know which to pick. Then there’s setting up the certificate with the dns provider. So I got nginx working with a certificate but gave up after the VM running Jellyfin couldn’t see it. Googling showed someone on Reddit with the same problem but no answer other than others saying “works for me”
Beside, that wasn’t even the topic. We were discussing - or rather, I was proving to the above commenter - that setting up Jellyfin in a way that does not allow an intruder to crypto mine or host CSAM or use your device as a proxy, is incredibly easy.
Port setup and it’s perceived impossibility by you has naught to do with that topic.